See how far an attacker gets. Before a real one does.
SIMAPTIC safely runs real adversary campaigns against your firm and reports what your defenses caught and what they missed.
- Uses C2 for Safe Payloads
- MITRE ATT&CK Mapped
- Built by Red Team Veterans
- On-prem, Cloud, or Hybrid
Pick. Run. Remediate. Repeat.
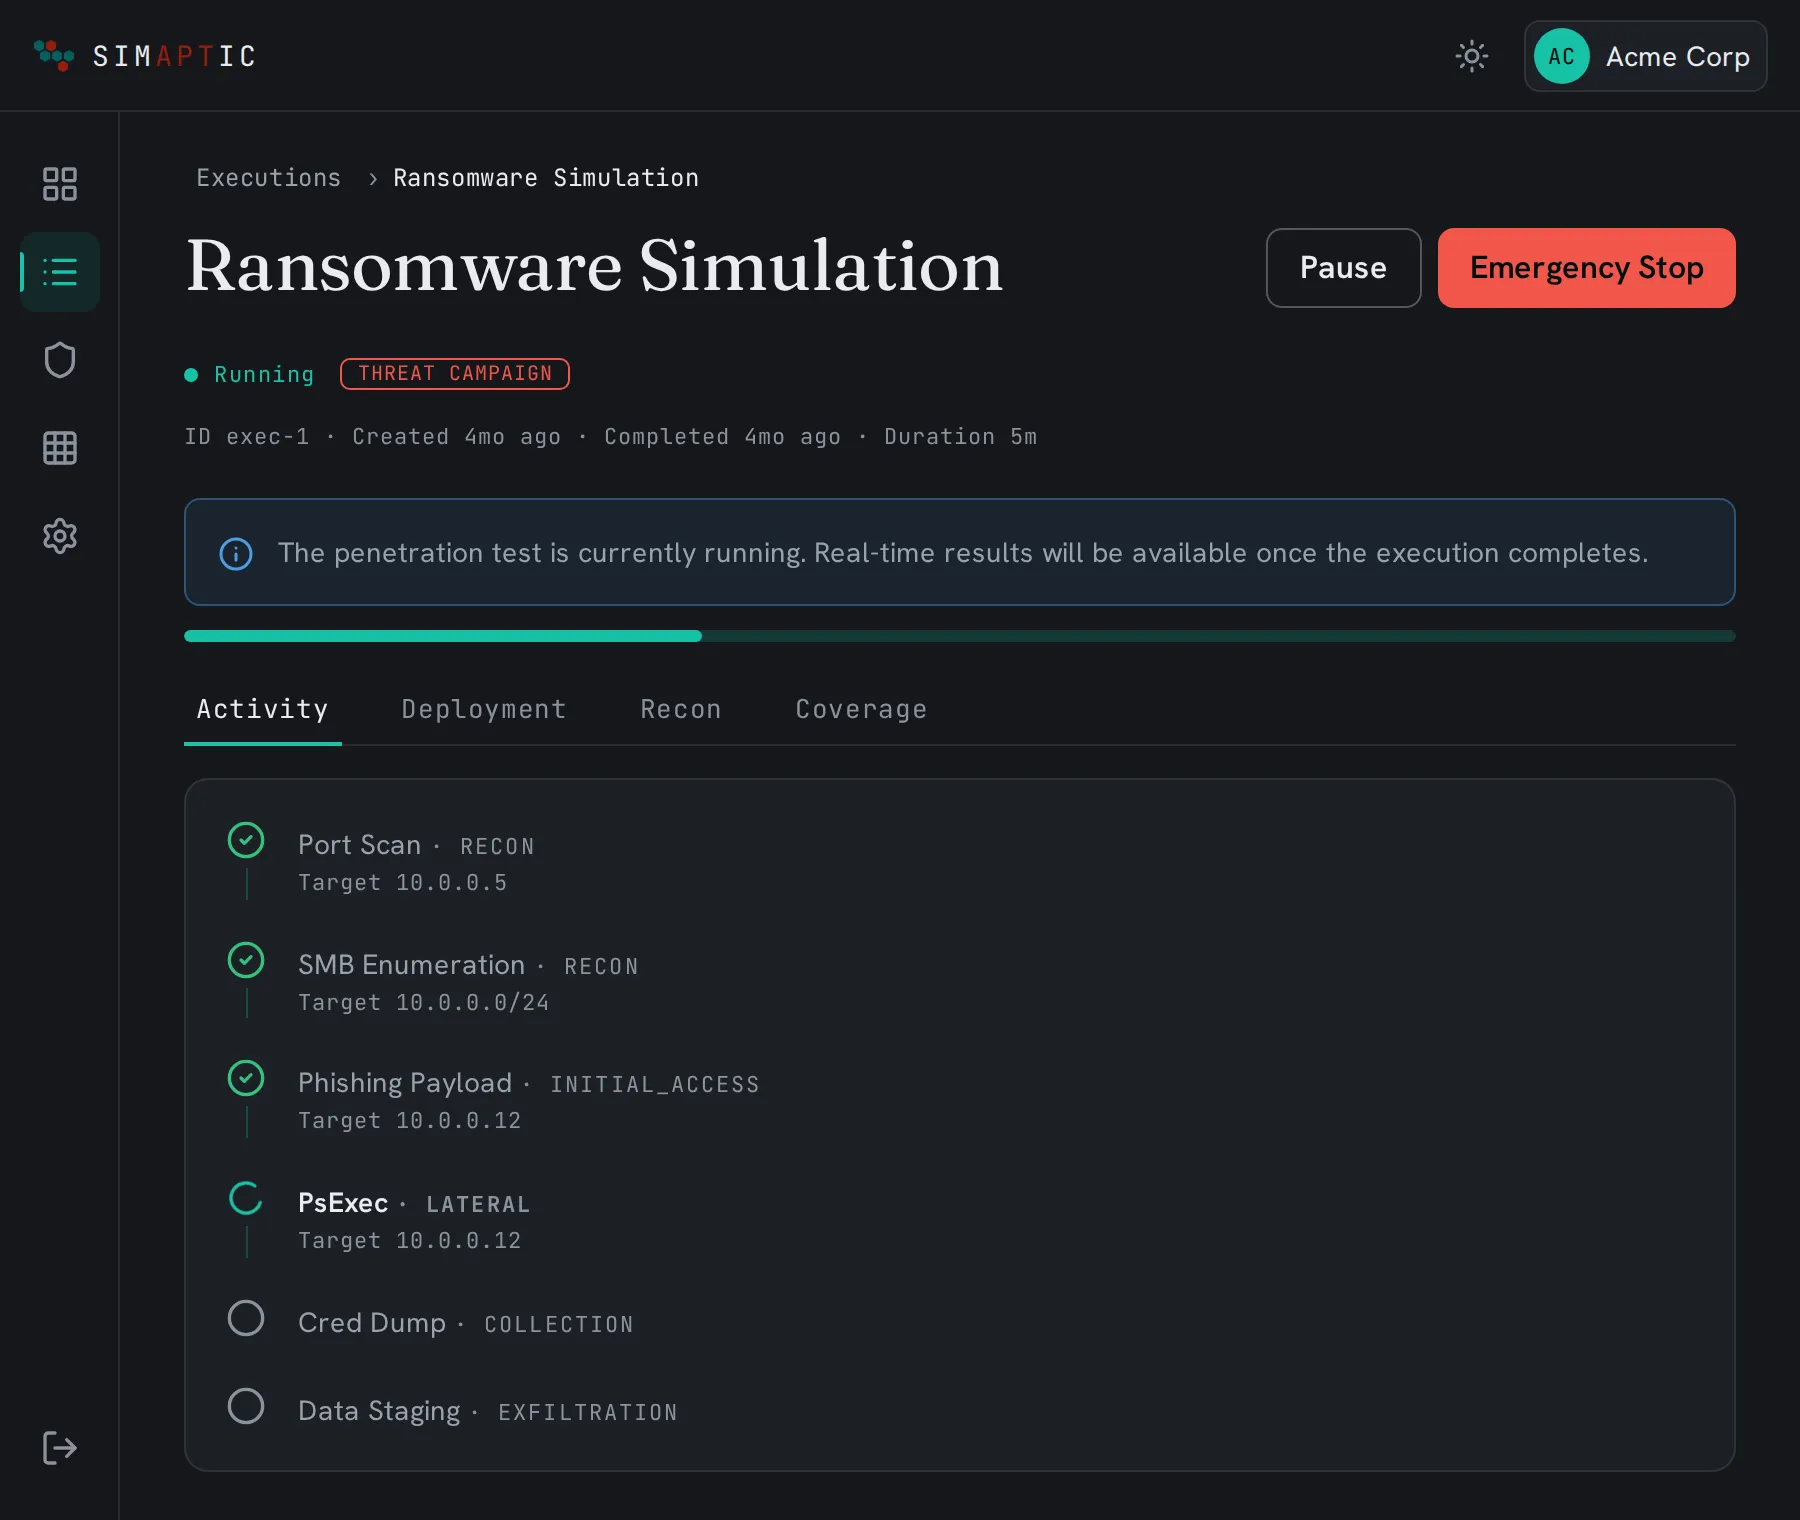
Choose a scenario, and AI agents do the rest — they plan the campaign, execute it live, and report exactly what your controls caught and what slipped through.
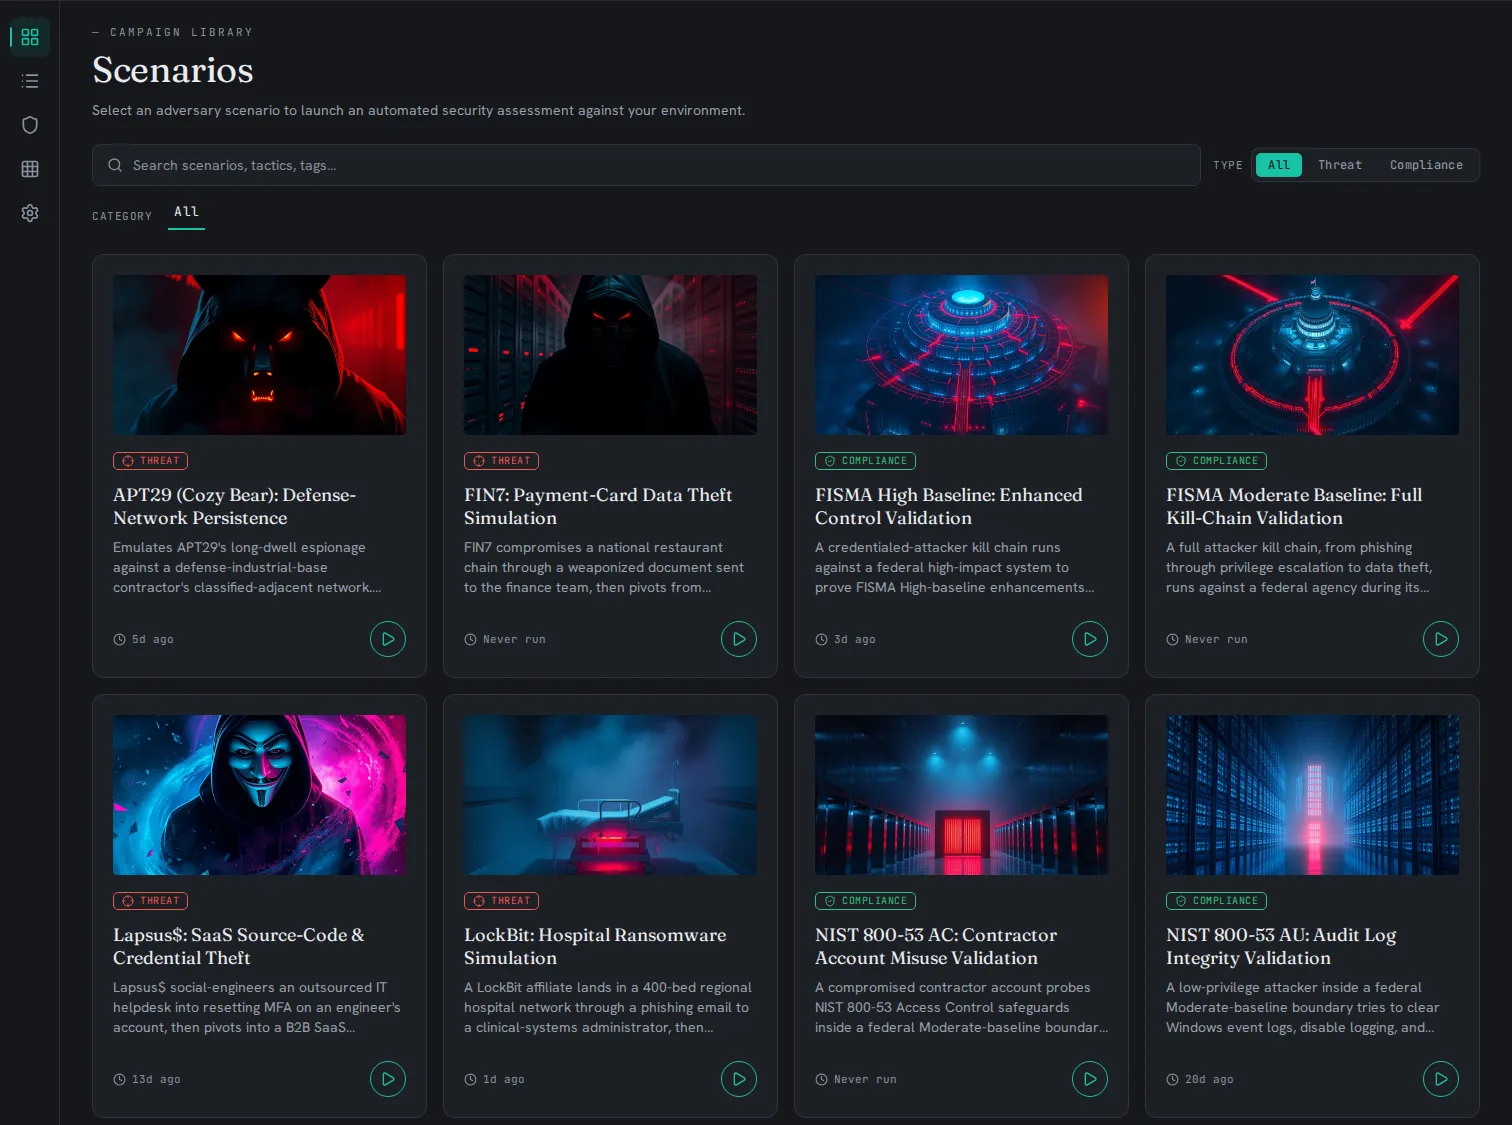
- Pick a scenario from the catalog: APT29, LockBit, or NIST 800-53.
- Run it: AI agents plan the campaign and execute it live against your defenses.
- Read the evidence: each control comes back fired or missed.
- Repeat after every meaningful change to prove the fix held.
A snapshot, a checklist, or a real attack.
An annual pentest is a snapshot, and a typical breach-and-attack tool that never leaves its checklist. SIMAPTIC runs a real attack you can repeat after every change.
| Annual pentest | Typical BAS tool | SIMAPTIC | |
|---|---|---|---|
| Runs real adversary tooling over live command-and-control | yes | no | yes |
| Actually exercises your EDR and detections | partial | no | yes |
| Grows new attack paths as it finds hosts | yes | no | yes |
| Repeatable after every change | no | yes | yes |
| Results mapped to compliance controls (Reg S-P, NIST) | partial | partial | yes |
| Priced for firms without a security team | no | no | yes |
Walk into the exam with the answer key
Reg S-P and SEC examiners now ask how you know your safeguards work. Every SIMAPTIC campaign maps to the controls you have to prove. Each control is tested by a real technique and comes back detected or missed, in a report you can hand to an examiner.
- A compliance framework such as NIST 800-53 defines the controls in scope.
- IA-5 Authenticator Management is tested by a Credential Access technique, and the result is detected.
- AC-6 Least Privilege is tested by a Privilege Escalation technique, and the result is missed.
- AU-6 Audit Review is tested by a Defense Evasion technique, and the result is detected.
Red Team Rigor without the Red Team Price
SIMAPTIC is built by veterans of offense and defense, and every campaign runs realistic command-and-control. You get the technique of a mature red team at a flat, small-firm price, on-premises, cloud, or hybrid.